

What you’ll end up with
Before you begin
You need:- An Okta admin who can create app integrations and assign admin roles — someone who can create an API Services app under Applications and grant it the Read-only Administrator role.
- An Origin admin account — only Origin admins can create directory integrations.
- Your Okta domain — the host you sign in to (for example
yourorg.okta.com). European (.okta-emea.com) and preview (.oktapreview.com) orgs are also accepted.
Setup steps
1
Start a new Okta integration in Origin
- Sign in to the Origin dashboard.
- Click Admin in the left sidebar, then select Identity.
- Click Add Integration.
-
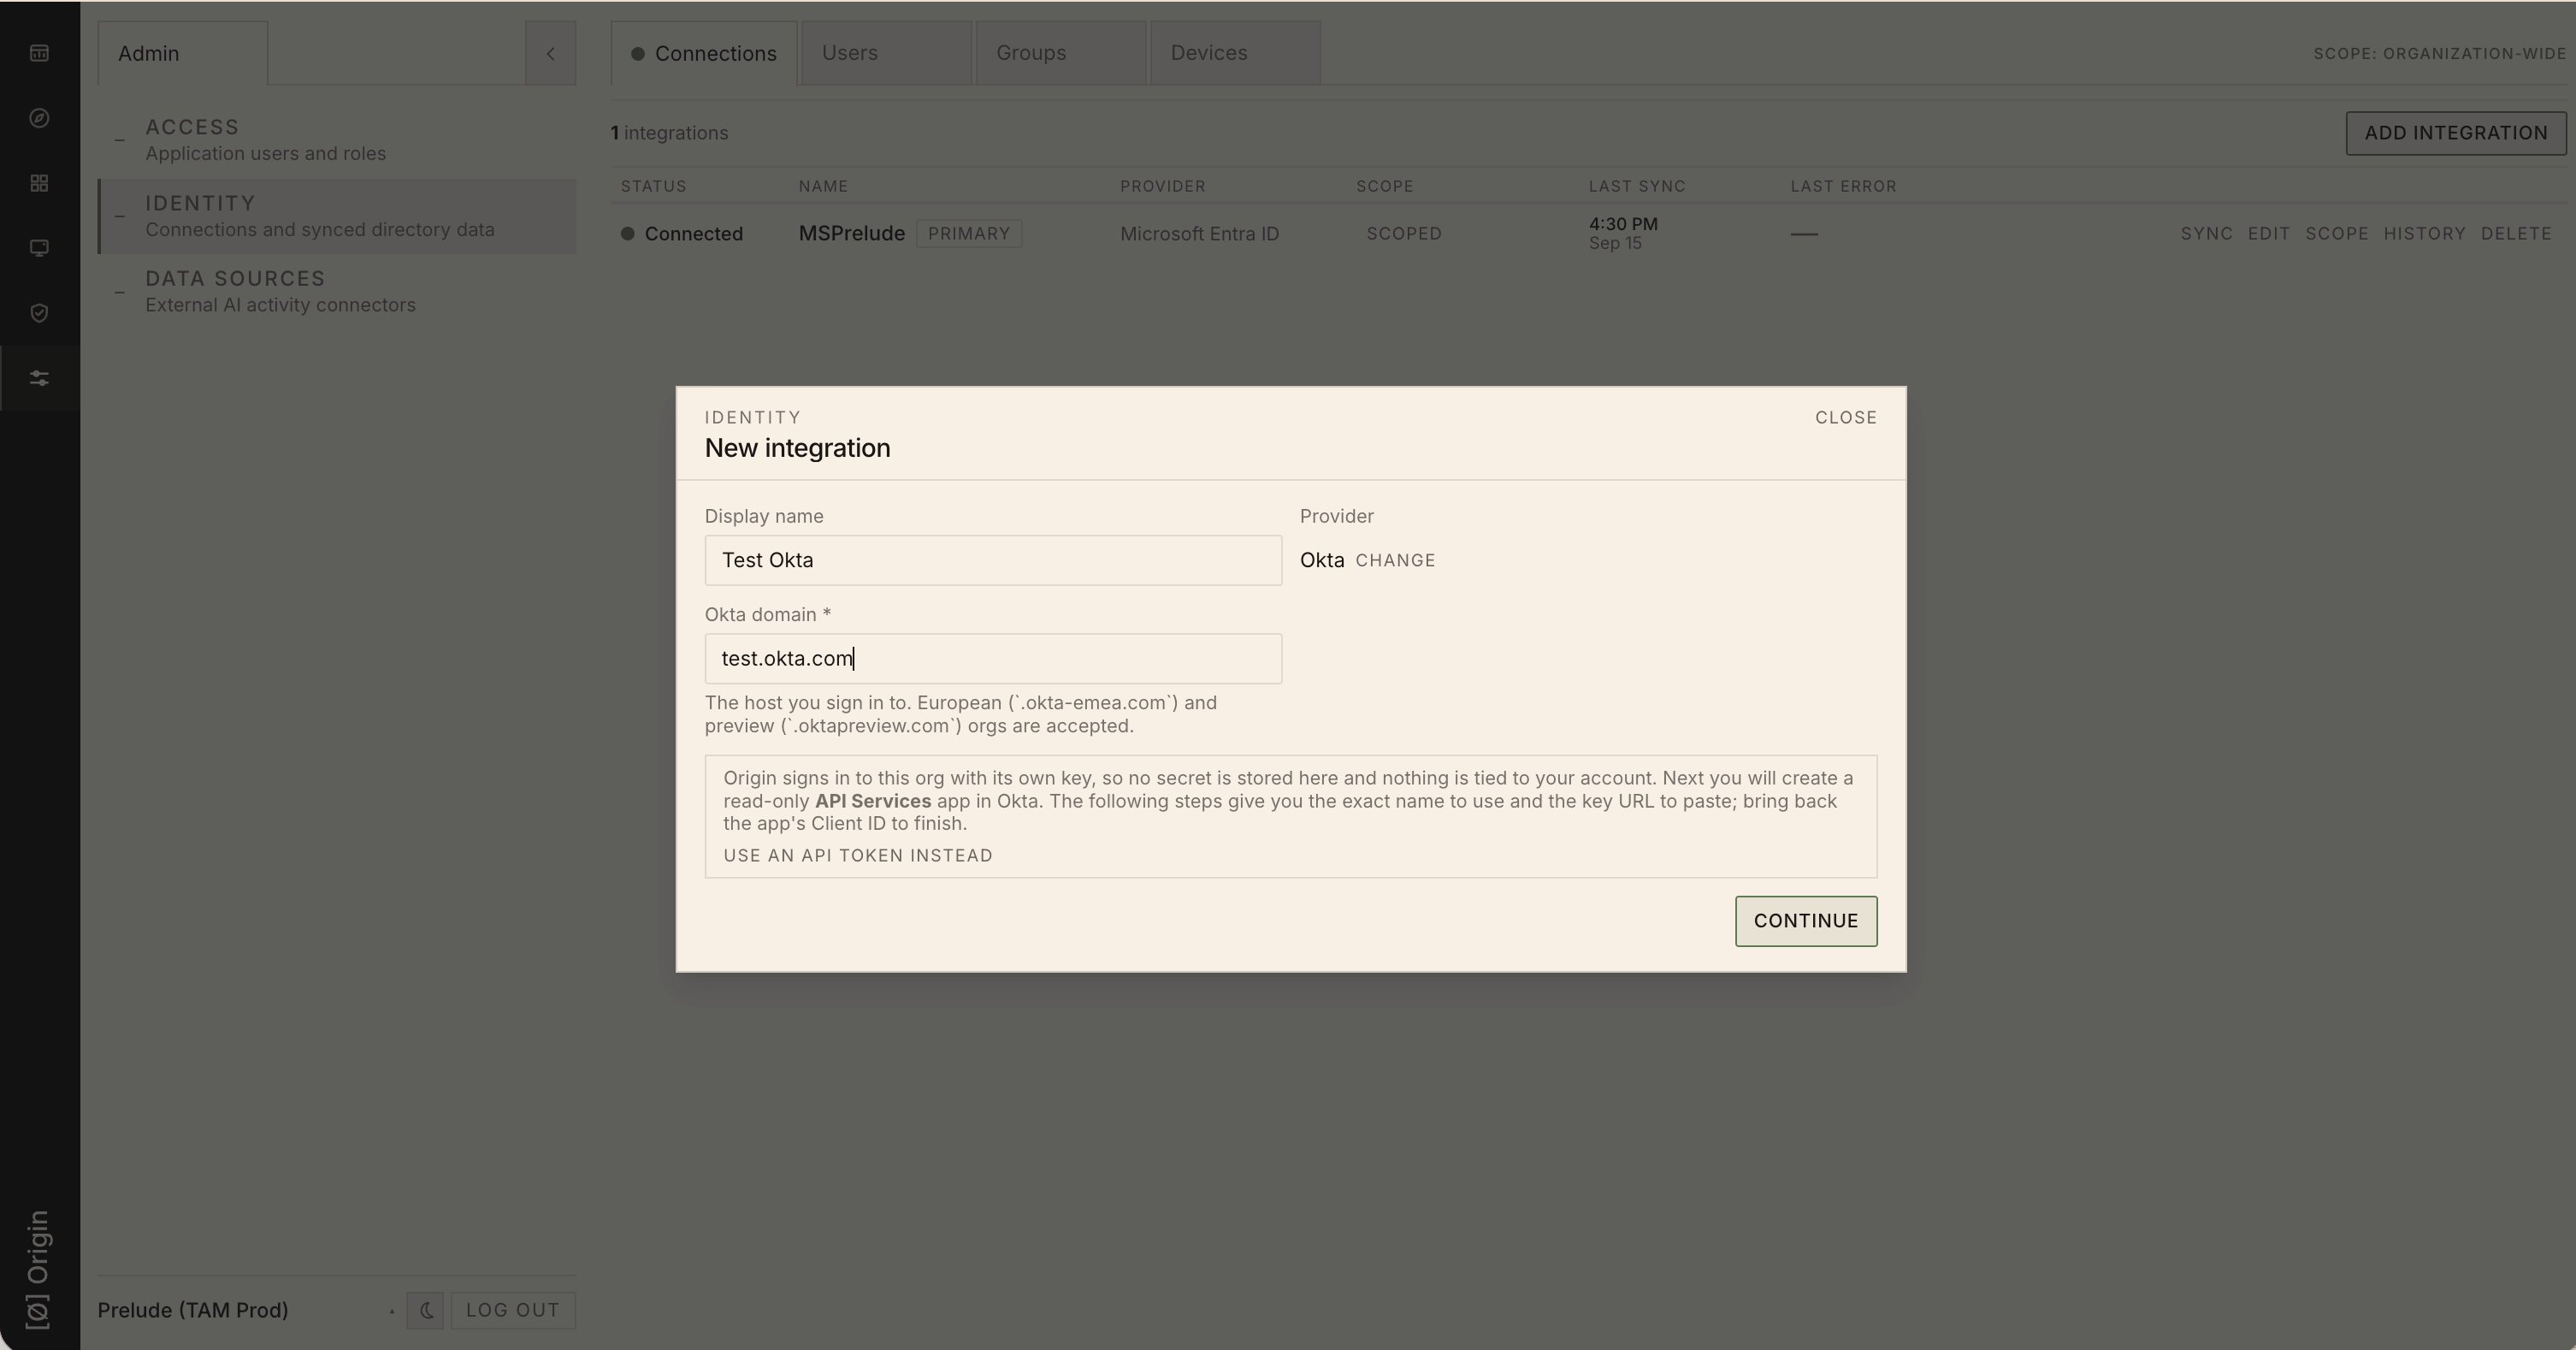
In the New integration dialog:
- Display name — a label for this integration, e.g.
Okta. - Provider — set to Okta (use Change if it isn’t already selected).
- Okta domain — enter your Okta host, e.g.
yourorg.okta.com.
- Display name — a label for this integration, e.g.
-
Click Continue.
2
Create the API Services app in Okta
Origin now shows a Finish setting up in Okta panel with the exact values to use. Keep this panel open — you’ll come back to it after saving the app in Okta.
- In your Okta domain, go to Applications → Create App Integration → API Services.
-
Name it exactly the app name Origin generated (e.g.
origin-0ed37d524d3a). Connecting reads the name back to confirm you own the org, so it must match character for character. Click Copy next to App Name in Origin to avoid typos.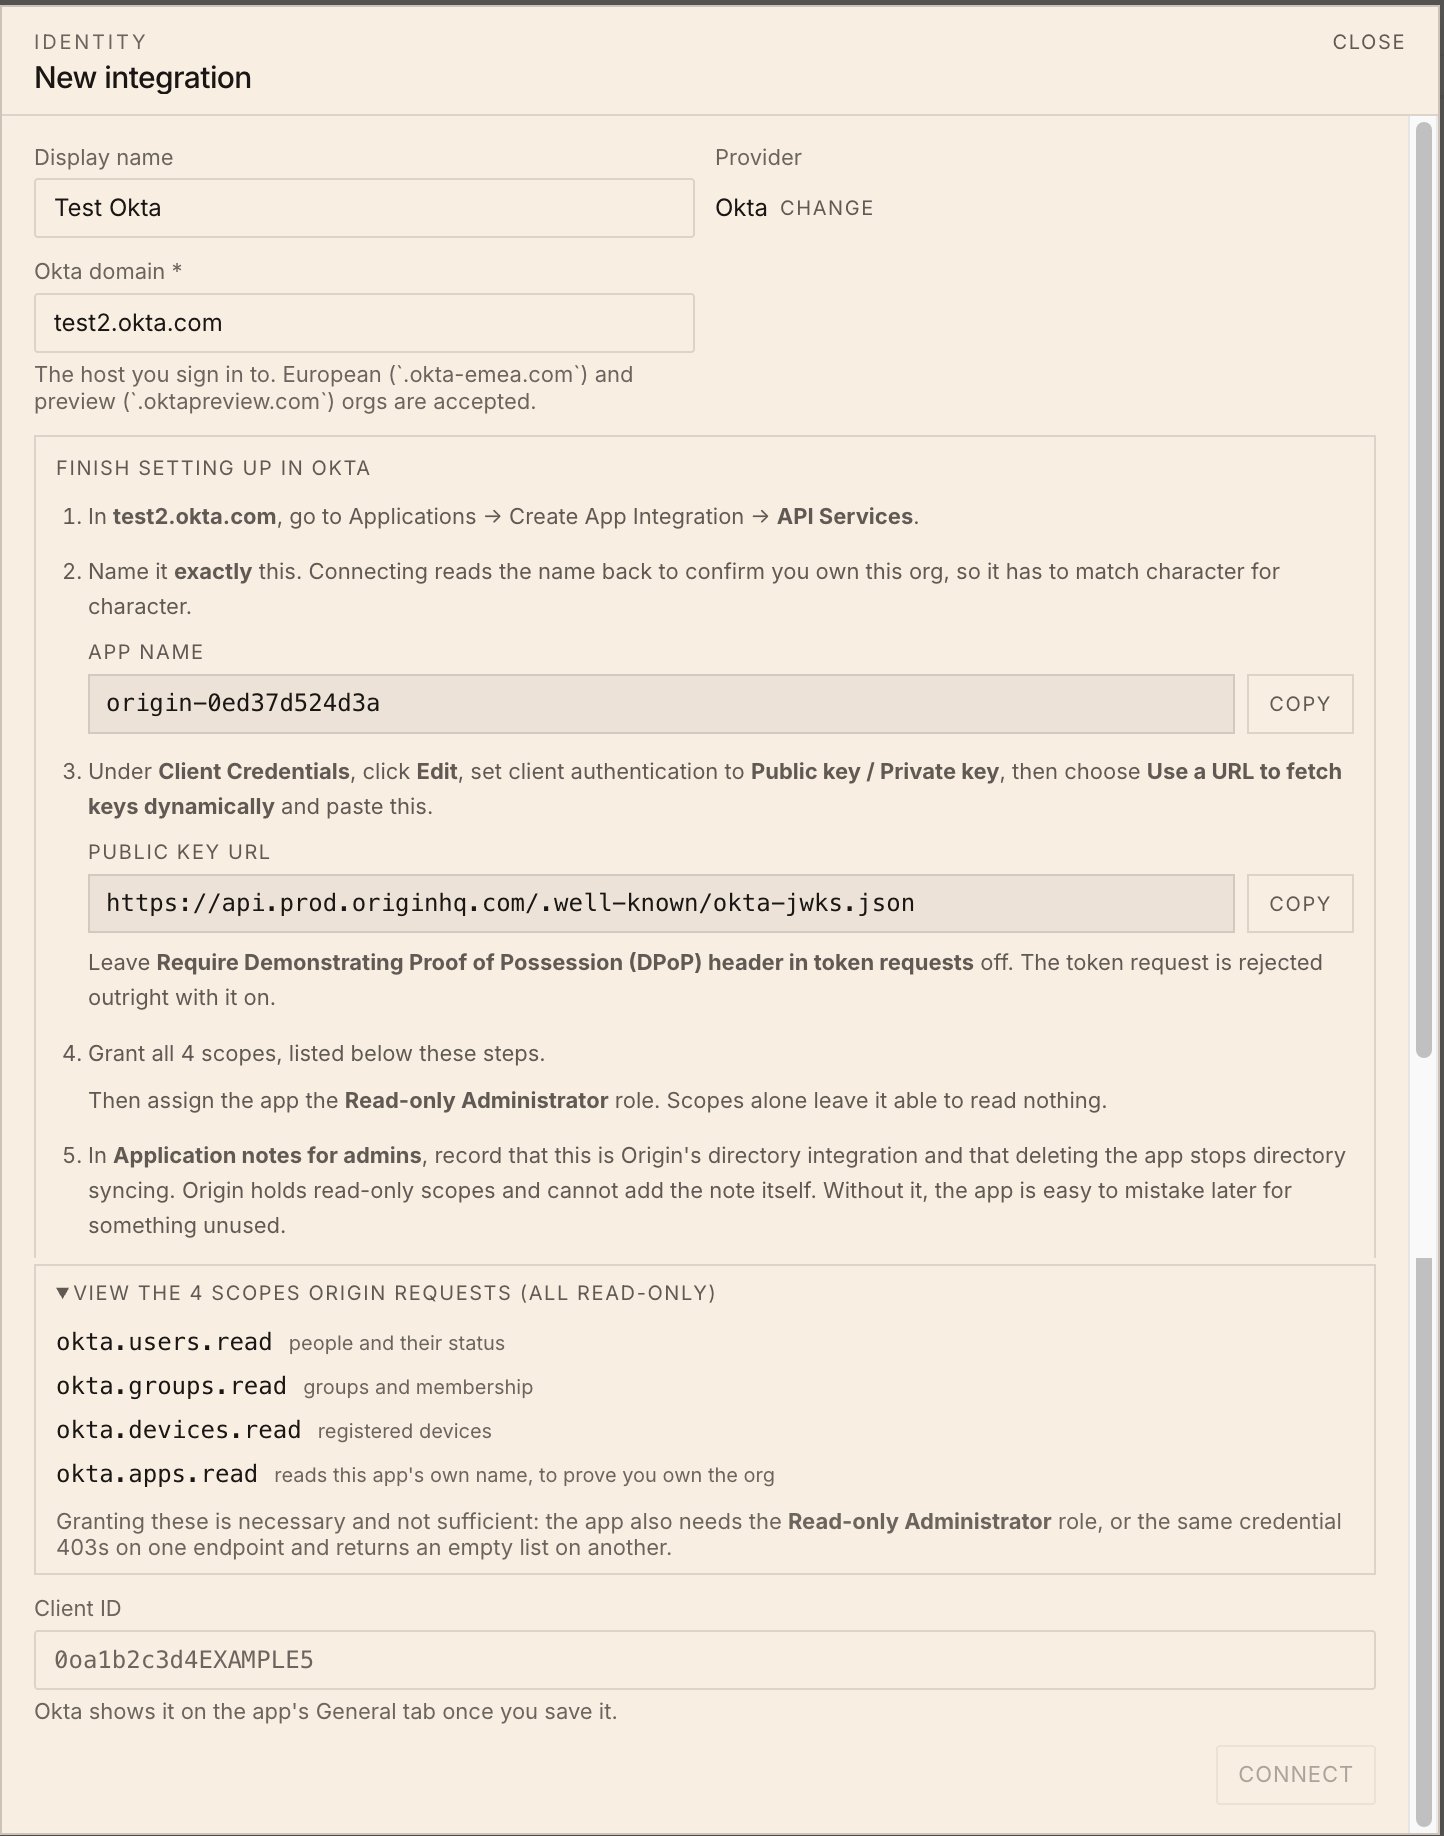
3
Configure client authentication
Still on the new app in Okta:
- Under Client Credentials, click Edit.
- Set Client authentication to Public key / Private key.
- Choose Use a URL to fetch keys dynamically and paste the Public Key URL Origin gave you:
- Leave Require Demonstrating Proof of Possession (DPoP) header in token requests off. Okta rejects the token request outright if it’s on.
4
Grant scopes and the admin role
- Grant the app all four scopes below (all read-only):
- Assign the app the Read-only Administrator role. Granting the scopes above is necessary but not sufficient on its own — without the admin role, the same credential 403s on some endpoints and returns an empty list on others.
- In Application notes for admins, add a note that this app is Origin’s directory integration and that deleting it stops directory syncing. Origin holds only read-only scopes and can’t add this note itself — without it, the app is easy to mistake later for something unused.
- Save the app.
5
Finish connecting in Origin
- Okta shows the app’s Client ID on its General tab once you save it. Copy it.
- Back in Origin’s New integration dialog, paste it into the Client ID field.
- Click Connect.
6
Verify in the Directory Browser
From Admin → Identity, the integration row should show Status: Connected, with Provider: Okta and a recent Last Sync time.Then check the Directory Browser:
- Users — should list everyone in your Okta org. Click any user to see their direct groups.
- Groups — click any group to see its direct user members and sub-groups.
- Devices — registered devices resolve an Owner against the synced users.
What gets synced (and what doesn’t)
Synced:- Users (active and suspended) — profile fields, status, group memberships.
- Groups — name, description, membership, and nesting.
- Devices registered in Okta — device name, platform, and assigned user.
- Okta applications, sign-on policies, or authentication policies.
- MFA factors or credentials.
- Any Okta System Log / audit data.
Managing the integration
- Rotate: Origin’s authentication key is managed on Origin’s side and rotates automatically — there’s no customer-side secret to rotate. If you need to re-establish trust (for example, after editing the Okta app), re-open Add Integration to regenerate the app name and Client ID pairing.
- Remove: Delete the integration from its row in Admin → Identity. Syncing stops; data already in Origin follows your tenant’s retention settings. To fully revoke access on the Okta side, delete the API Services app from Applications in Okta.
Troubleshooting
Connecting fails with an app name mismatch
Connecting fails with an app name mismatch
The app name in Okta doesn’t exactly match the name Origin generated. Reopen the integration’s setup panel in Origin, copy the App Name again, and rename the Okta app to match it character for character (including the
origin- prefix and casing).Token requests fail after configuring Public key / Private key auth
Token requests fail after configuring Public key / Private key auth
Confirm Require Demonstrating Proof of Possession (DPoP) header in token requests is off — Okta rejects the token request outright with it on. Also confirm the Public Key URL was entered exactly as
https://api.prod.originhq.com/.well-known/okta-jwks.json, with no trailing characters.Connect succeeds but Users/Groups/Devices are empty, or some endpoints 403
Connect succeeds but Users/Groups/Devices are empty, or some endpoints 403
The app is missing the Read-only Administrator role. The four
okta.*.read scopes alone aren’t sufficient — assign the role in the app’s Admin roles tab in Okta, then trigger a sync again.Can't find the Client ID to paste into Origin
Can't find the Client ID to paste into Origin
Okta only shows the Client ID on the app’s General tab after you save it. If you closed the app before saving, reopen it from Applications in Okta — the Client ID is stable and doesn’t change on subsequent visits.